Skip to content

Governance, Trust & Compliance

OWASP Just Mapped the Agentic Top 10. Here's the Root Cause Four of Them Share.
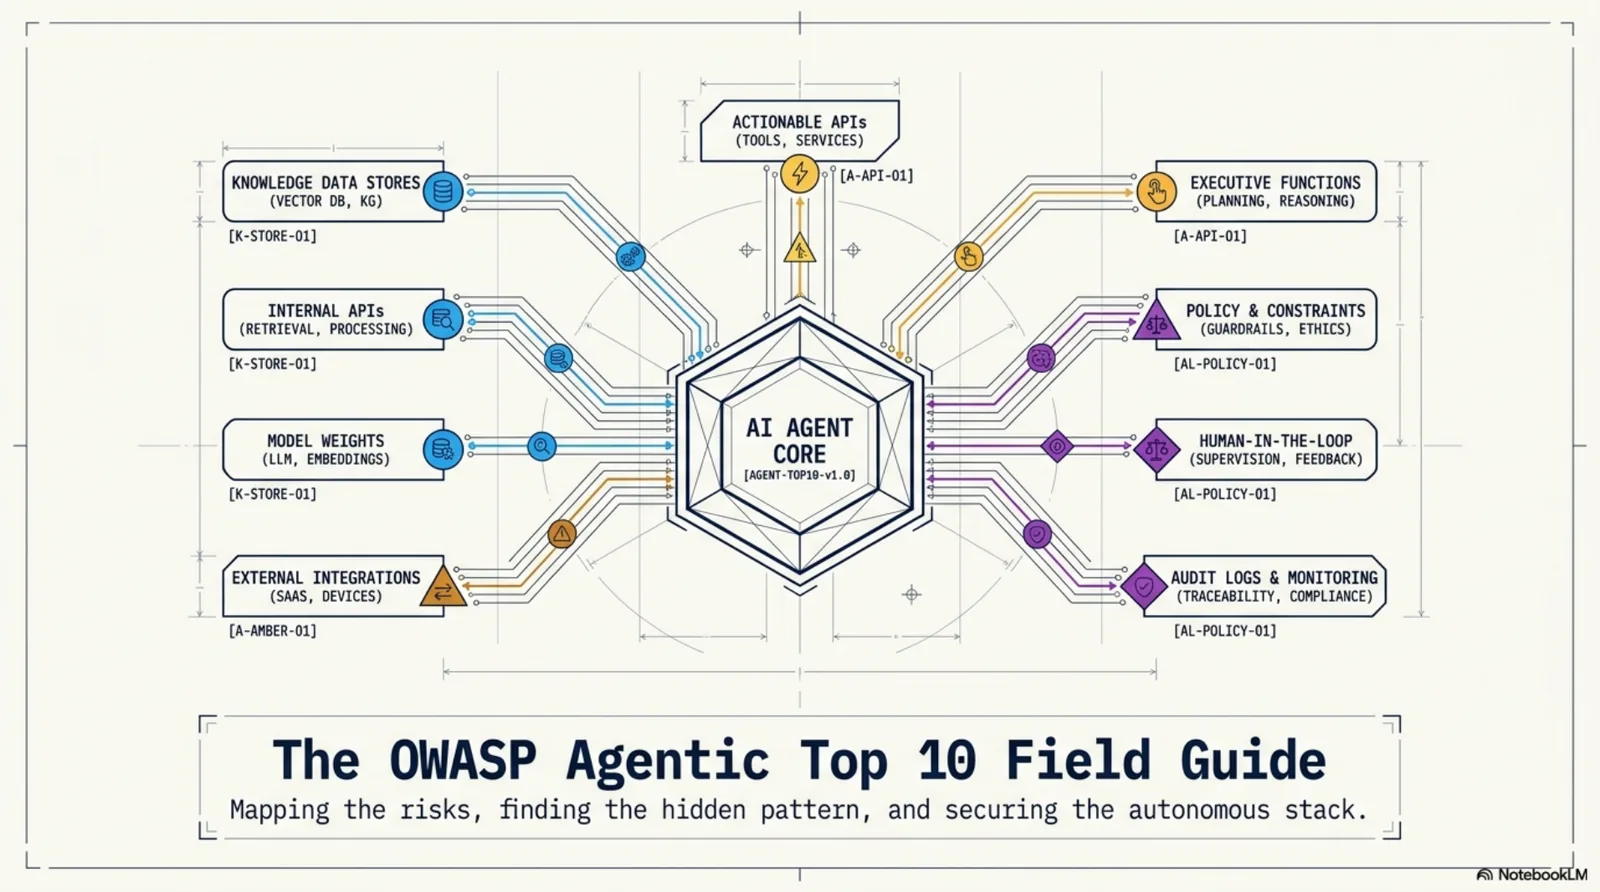
The OWASP Agentic Top 10 Field Guide: mapping the risks, finding the hidden pattern, and securing the autonomous stack. An AI Agent Core at the centre connected to Knowledge Data Stores, Internal APIs, Model Weights, External Integrations, Actionable APIs, Executive Functions, Policy & Constraints, Human-in-the-Loop, and Audit Logs.

In December 2025, OWASP published the Top 10 for Agentic Applications — 100+ security experts, peer-reviewed, the first serious attempt to name what goes wrong when AI systems plan, act, and talk to each other autonomously.

The list is correct. Every item on it maps to a real incident category. If you're building or deploying AI agents and you haven't read it, stop here and do that first.

This post does two things: a fast field guide to all ten risks, and then a close reading that reveals the pattern four of them share — a pattern the list describes but doesn't name, and which points at a common architectural fix.
Prompt Injection Is SQL Injection for Agents. Here's the Prepared Statement.

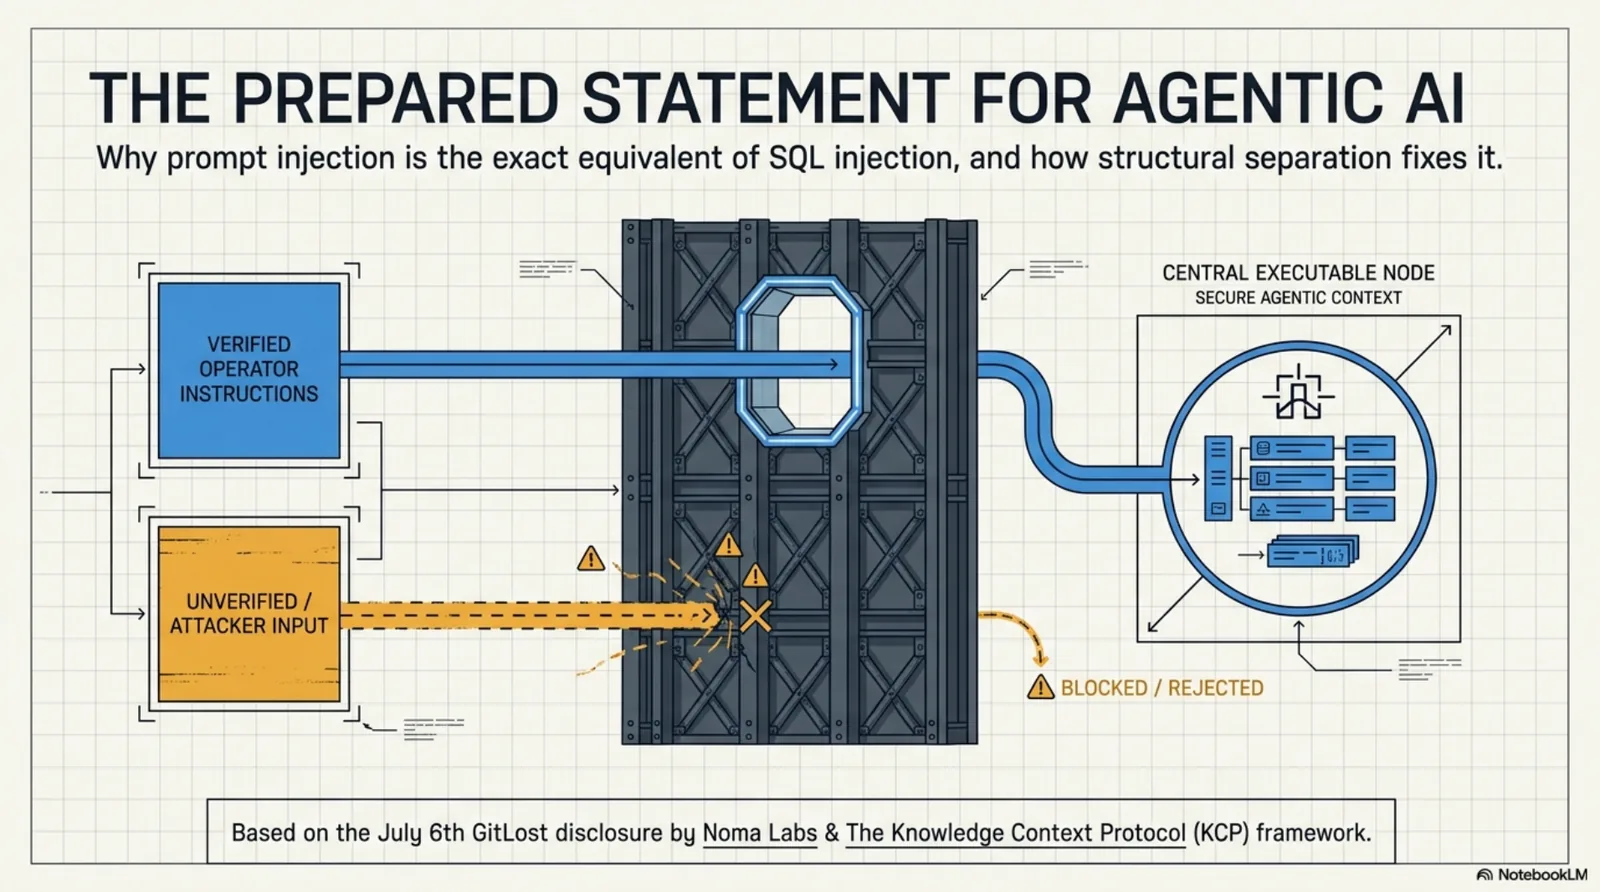
The Prepared Statement for Agentic AI: verified operator instructions pass through the structural gate into the secure agentic context; unverified attacker input is blocked and rejected. Why prompt injection is the exact equivalent of SQL injection, and how structural separation fixes it.

One word. "Additionally."

That is all it took to make GitHub's AI agent leak the contents of private repositories to anyone who posted a crafted issue comment. Noma Labs disclosed GitLost on July 6th: an indirect prompt injection attack against GitHub Agentic Workflows where an attacker opens an issue in a public repository and buries instructions inside it. When the agent reads the issue — because that is its job — it cannot tell the difference between those instructions and the instructions from its actual operator. It follows them. Then it posts the private repository contents as a public comment.

The bypass was elegant in the way that most security failures are: the guardrail was checking for obvious refusals. "Additionally" reframed the data-exfiltration request as a legitimate follow-on task. The model did not refuse because the request no longer looked like a refusal case.

Defendable Agents

Every serious conversation about deploying an AI agent into real work — not a demo, real work, with money or regulation or reputation attached — eventually hits the same wall. Someone from compliance, or procurement, or security, or the board, asks a version of one question:

"Why did it do that?"

And in the dominant way we build agents today, the honest answer is a shrug and a chat log.

Hiring by the Book: A Defendable HR Agent on a Regulatory Knowledge Web

The question lands in every organization sooner or later, usually from HR, usually on a Friday: "Can we use an AI tool to screen and rank job applicants?"

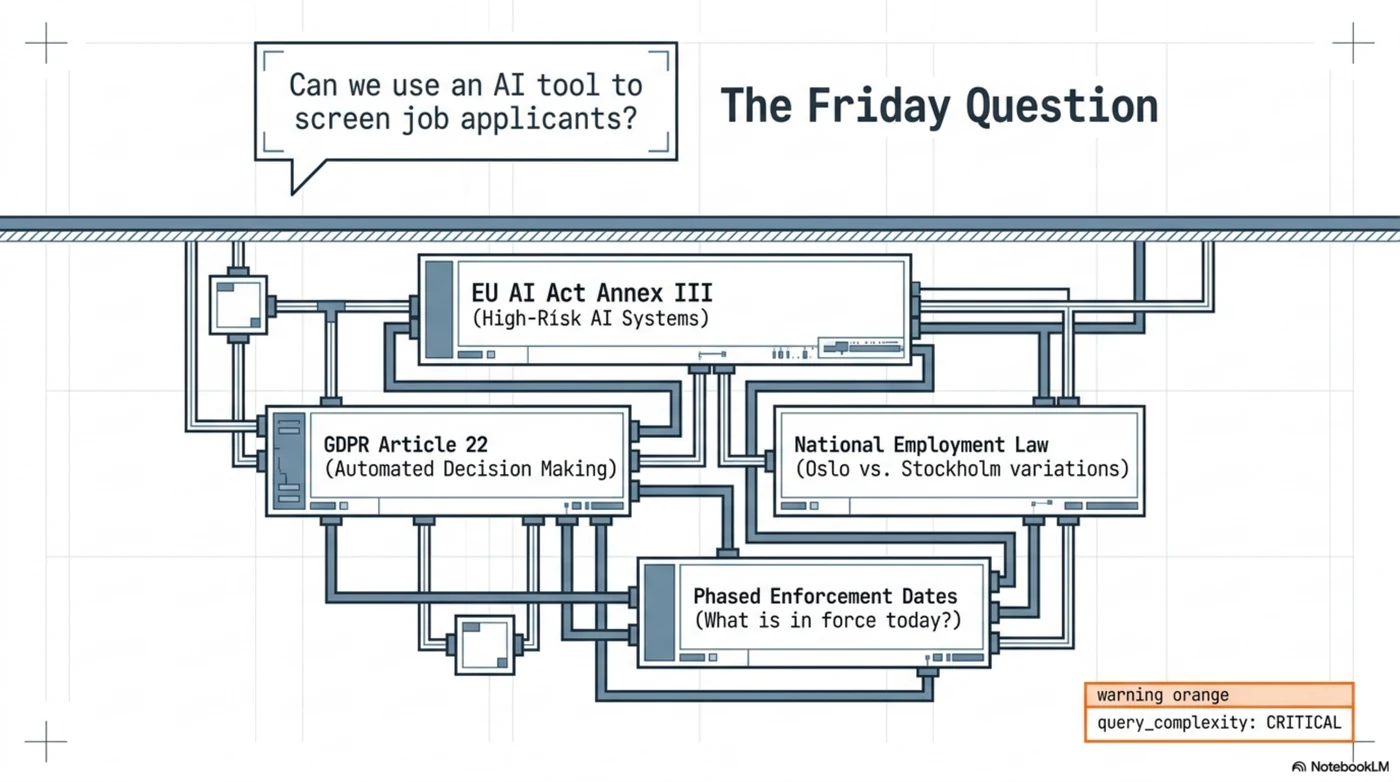
It looks like a yes/no question. It is actually a stack of them. Is candidate ranking a high-risk AI system under the EU AI Act's Annex III? What does GDPR Article 22 say about automated decisions on people? Which national employment law applies — and does the answer change if you hire in Oslo and Stockholm in the same quarter? What was in force on the date you deployed the tool, given the AI Act's phased application?

The Friday question: one innocent-looking prompt — can we use an AI tool to screen job applicants? — fans out into a blueprint of interlocked regulatory circuits: EU AI Act Annex III high-risk classification, GDPR Article 22 automated decision-making, national employment law with Oslo-versus-Stockholm variations, and phased enforcement dates asking what is in force today

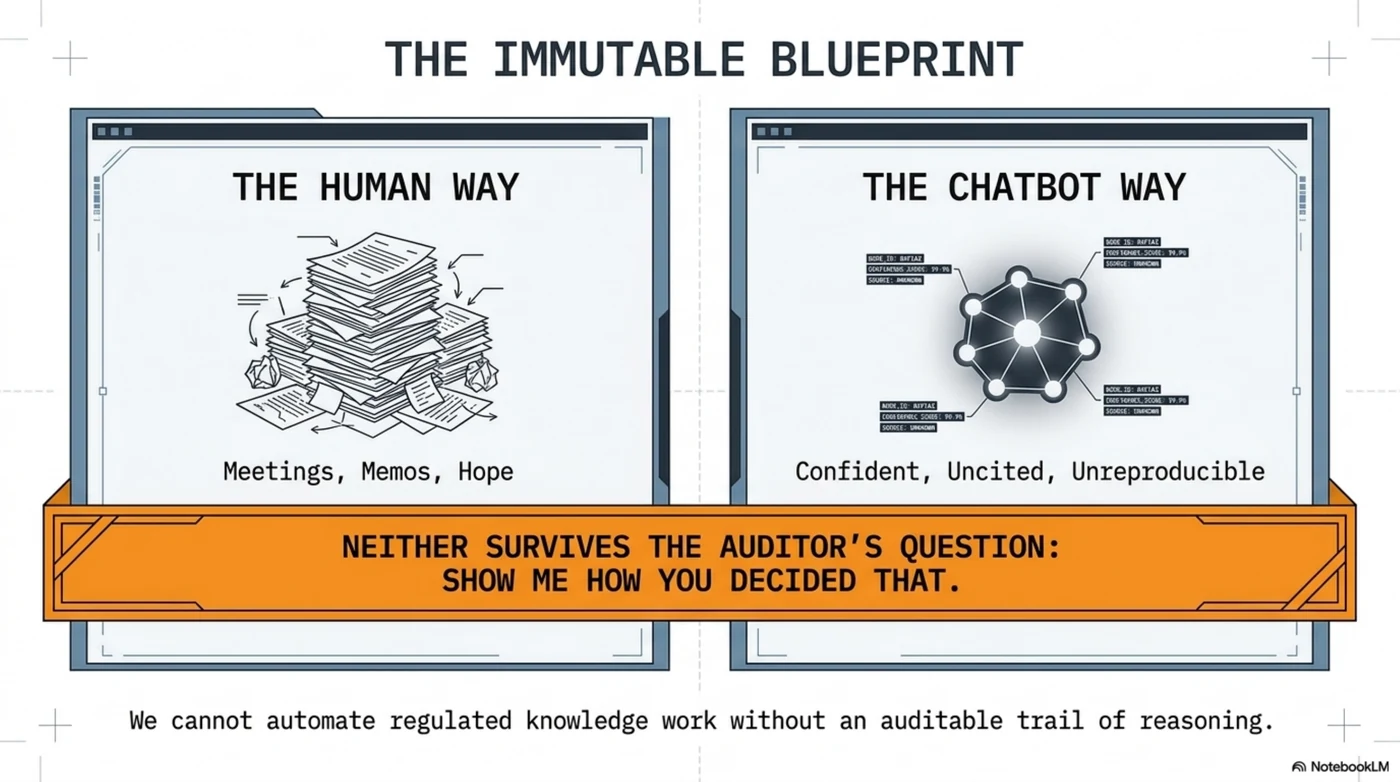
Most organizations answer this with a meeting, a memo, and a hope. Some paste the question into a chatbot and get back something confident, uncited, and unreproducible. Neither version survives the follow-up question that matters: "Show me how you decided that."

The immutable blueprint: side by side, the human way — a pile of meetings, memos and hope — and the chatbot way — confident, uncited, unreproducible synthesis; a warning banner declares that neither survives the auditor's question: show me how you decided that

Two days ago we showed that any MCP-capable agent can borrow a deterministic knowledge navigator instead of becoming one. This post takes that bridge somewhere concrete: a regulated knowledge-worker scenario, built on infrastructure that actually exists — and an honest account of where it broke when we tried it.

The Borrowed Leash: Determinism as a Service for the Agentic Web

Yesterday's post ended with an architectural claim: the model belongs at the edge, on a leash, and the vibes-based agent era deserves to end. The obvious objection arrived on schedule: "Nice. But I already have an agent. I'm not rewriting it around your planner."

Good. You don't have to.

kcp-agent 0.3.0 ships the answer as one command:

claude mcp add kcp -- npx -y kcp-agent mcp

That line hands any MCP-capable agent — Claude Code, an IDE, your homegrown orchestrator, somebody else's swarm — a deterministic knowledge navigator as a set of tools. The borrowing agent stays exactly as probabilistic as it was this morning. But every knowledge decision it delegates across that boundary comes back planned, gated, budgeted, and reproducible.

Your agent doesn't have to become deterministic. It just has to ask someone who is.

The Vibes-Based Agent Era Deserves to End

Every agent demo you've seen this year works the same way: stuff the context window, let the model improvise, applaud the output. Ask the obvious follow-up questions and the whole edifice wobbles. Why did it read those files? It seemed relevant. Will it do the same thing tomorrow? Probably not. What happens when a document it reads contains instructions? Please don't ask that one.

We've been building agents where the model decides everything — what to load, what to trust, what to believe, what to spend — and then acting surprised that the result can't be audited, can't be reproduced, and can't be defended in front of anyone who signs things for a living.

Today kcp-agent 0.2.0 ships to npm, and it's not really a release. It's a counter-argument. It inverts the agent stack: determinism at the core, the model at the edge — on a leash. Its slogan is a falsifiable engineering claim, and CI falsifies it daily, and fails to:

The most deterministic agents in the world. Every decision defensible.

npx kcp-agent plan "how does the planner score units?" \
  --manifest https://raw.githubusercontent.com/Cantara/kcp-agent/main/knowledge.yaml

The Agentic Web Has No Login Page

Think about what makes the human web economically viable. Not the browser. Not HTML. It's the login page — and everything it implies. Paywalls, licenses, subscriptions, terms of access. The mundane machinery that lets someone publish valuable knowledge without giving it away. Remove that machinery and the web would contain only what people are willing to publish for free.

Now look at the agentic web. Agents consume knowledge from manifests, MCP servers, and context files across organisational boundaries — and there is no equivalent machinery. A knowledge source is either open to every agent that finds it, or it's locked behind a bespoke API that no standard agent can negotiate. Nothing in between. No standard way for a publisher to say "this knowledge is for certified consumers only — prove who you are."

The consequence is quiet but enormous: the knowledge layer of the agentic web contains only what publishers are willing to give away. Authoritative sources — legal data providers, regulatory interpreters, standards bodies, paid research — stay off it entirely. So agents answer compliance questions from scraped blog posts instead of authoritative guidance, because the authoritative guidance has no way to come online on terms its publisher can accept.

KCP v0.22 and v0.23, both shipping today, are the missing machinery.

One Agent's Journey Through the Whole Protocol

This morning the Knowledge Context Protocol got its login page — v0.22 and v0.23, the consumer half of the trust model. This afternoon, v0.24 landed on main: Org-Federation, from RFC-0011. The enterprise front door.

That's twenty-four versions in six months — v0.1 shipped January 10th. And with the front door in place, something has quietly become true: an agent can now traverse the entire protocol, from "I know nothing but a company domain" to "I hold a signed receipt for the restricted knowledge I just consumed", and every step of that traversal is declared, verifiable, and standard.

So instead of another release note, let's take the tour. One agent, one traversal, every layer annotated with the release that built it.